Integrating C2PA and verification badges into a CMS: workflow guide
Design a CMS workflow with C2PA, APIs and verification badges across assets, versions, signing, CDN delivery, corrections and release checks.
Integrating C2PA into a CMS means designing how provenance claims are generated, preserved, and verified throughout a piece of content's journey. Adding a badge to the page is only the visible part: first you must define which asset is signed and how every version is handled.
This guide presents a reference architecture for editorial and technical teams. It is not documentation for a particular SCE API and does not assume that a plugin automatically supports every format. Endpoints, compatibility, and features must be checked for the chosen integration. For WordPress and Salesforce, explore our no-code integrations.
First decision: what are you making verifiable?
A news page can contain a title, text, image, video, and attachments. They are not necessarily one cryptographic object. A photograph's credentials do not automatically attest to the headline or the claims in the article that embeds it.
Define the unit of verification: the published image file, a downloadable PDF, or a versioned representation of the editorial content. If you want to verify several elements, document the relationships among them. This choice determines what you sign, what you retain, and what you show the reader.
The C2PA guide explains the roles of assets, manifests, and signatures. Formats and viewers do not all offer the same support, so testing must cover the actual combination used by your website.
Map CMS transformations
Before writing an integration, list every step that can change an asset. An editor may crop it, the CMS may compress it, and the CDN may convert it to another format. Even a download with an optimization option may not return the original bytes.
| Step | Question to answer |
|---|---|
| Import into the media library | Are the original file and its credentials retained? |
| Cropping and correction | Is the derivation recorded by a compatible tool? |
| Creation of responsive variants | Which versions receive a valid credential? |
| CDN distribution | Does the file served to the reader retain a verifiable binding? |
| Download or sharing | Which version is delivered, and with which information? |
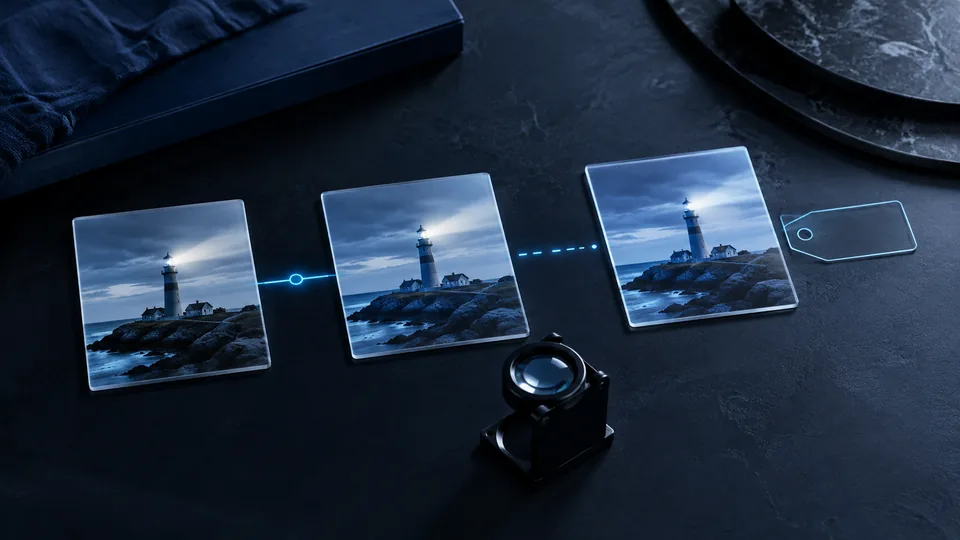
The C2PA specification describes how to link ingredients and later processing. Preserving history requires a workflow designed to do so; a signature in the first file is not enough.
One possible publishing workflow
A controllable workflow begins with the draft and ends with a check of the content actually distributed. The sequence below is conceptual, not a ready-to-use API call.
- Preparation. The editor completes the text and assets. The system assigns stable identifiers to the content and version.
- Approval. The version for publication is closed and the provenance claims to include are selected without adding unverified information.
- Transformation and signing. Final variants are created with a compatible process. The signature must cover the correct asset, rather than an intermediate copy that is later changed without tracking.
- Proof registration. The backend stores references and operation status. Any notarization is a separate step with its own result.
- Publication. The CMS associates the version with the verification-page link and displays the badge in the appropriate context.
- Final check. A test downloads the asset from the public website and verifies that it follows the expected path. It also checks the badge, version, and displayed information.
The exact order depends on the technology; some workflows support external or recoverable credentials. The constant requirement is to verify the result after the last transformation, not only before upload.
Keep signing operations out of the frontend
Readers' browsers should be able to open verification without receiving private service credentials. Signing keys and API secrets must not be embedded in the site's public code. Authorized operations belong in a backend or a signing component designed for that purpose.
The CMS can store a proof identifier, version, and operational status. The badge uses the public reference to open the correct page. Simply loading the widget should not decide that content is “verified.”
Before release, also agree on which data is actually needed in public claims. Not every detail available in the editorial system needs to be placed in the distributed credential.
Handle errors, waiting states, and updates
A signature or record may take time or fail. Design distinct states: draft, processing, completed, error, and superseded. If a check has not completed, the interface must not present it as successful.
Repeated requests should be handled consistently so a retry does not create duplicate proof or associate the result with the wrong version. Before retrying, the system must be able to recognize the original operation and check its status according to the chosen API's capabilities.
An editorial correction creates a new object to verify if it changes the attested content. Preserve the connection to the previous version, update public references, and invalidate relevant caches. With blockchain notarization, earlier proof continues to refer only to the old fingerprint.
Design an understandable badge
The text accompanying a badge should state what is verified: “Image provenance” is more precise than a generic promise about the entire page. The link should work with a keyboard, have an accessible name, and remain recognizable on mobile.
The verification page should clearly present the asset or version, signer when available, completed checks, and any missing information. A Content Credential is useful to readers only if they can interpret its results.
Checklist before launch
- Verify at least one file for every format and each variant served by the CDN.
- Make a change after signing and confirm that the result does not remain misleadingly positive.
- Simulate a network error: the CMS should distinguish waiting, error, and completion.
- Open an old link after a correction and check which version appears.
- Confirm that the proof can be exported and the original file is retained.
- Test the badge on mobile, with a keyboard, and without relying solely on color.
Frequently asked questions
For a concrete editorial example, apply the workflow to a verifiable digital press kit. If a variant loses the expected information, follow the Content Credentials not found troubleshooting guide.
Do I need to change CMS?
Not necessarily. Whether you can integrate the workflow depends on extensions, APIs, and control over transformations. Begin with a limited editorial workflow and measure its results before extending it to all content.
Can I sign only the main image?
Yes, if the chosen format and tools support it. The interface must make clear that the credential applies to that image, without extending the conclusion to the entire article.
Does C2PA conformance guarantee my workflow?
The C2PA conformance program is a reference for participating products. It does not replace testing of your complete chain: CMS, transformations, distribution, and interface must still be checked together.
Sources and further reading
Technical and editorial references consulted for this guide. Examples are illustrative and do not document real cases or specific integrations.