AI Act and C2PA: how transparency is changing for AI-generated content
The AI Act requires machine-readable marking for AI-generated content. Learn how C2PA, watermarks, labels and Content Credentials fit together.
From 2 August 2026, transparency around synthetic content is also a regulatory requirement. Article 50 of the AI Act requires providers of certain generative systems to make their outputs detectable as artificially generated or manipulated. For businesses, media organisations and platforms, simply placing an “AI-generated” label beneath an image does not address the whole issue.
The emerging framework distinguishes at least two layers: technical marking for machines and verification tools, and disclosures that people can perceive. C2PA and Content Credentials can support the first layer, but they are not the only permitted technology and they do not replace the visible disclosure requirements that apply to deepfakes.
What Article 50 of the AI Act requires
The European Artificial Intelligence Act assigns different responsibilities to providers and deployers.
Providers of systems that generate synthetic audio, images, video or text must ensure their outputs are marked in a machine-readable format and detectable as artificially generated or manipulated. As far as technically feasible, the solutions must be effective, interoperable, robust and reliable, taking into account the state of the art, implementation costs and the characteristics of the content.
The rules include exceptions, such as when a system performs an assistive function for standard editing without substantially altering the input data or its meaning. Deciding whether a specific case falls within the obligation therefore requires an assessment of both the system and its use, not just the final file format.
Deployers have disclosure obligations in specific situations. They must disclose when images, audio or video constitute a deepfake and, subject to the relevant exceptions, when AI-generated or manipulated text is published to inform the public on matters of public interest.
Technical marking and visible disclosure are not the same thing
A machine-readable mark is designed for software, platforms and verification tools. It can help identify content as AI-generated or manipulated and carry information about the process used to create it.
A visible disclosure communicates directly with the person encountering the content. It may take the form of a label, badge or icon accompanied by understandable text. The European Commission has published a set of icons to make this communication more consistent, while making clear that using an icon does not, by itself, establish compliance.
| Layer | Primary audience | Examples | Limitation to remember |
|---|---|---|---|
| Technical marking | Machines and verification systems | Signed metadata, invisible watermarks and other machine-readable signals | It may be removed, unsupported or undetectable in some copies |
| Visible disclosure | People | Badges, icons, labels or accessible notices | It does not authenticate who applied the label by itself |
| Provenance | People and machines | Content Credentials, edit history and the signer’s declared identity | It verifies claims and integrity, not whether a depicted scene is true |
These layers can complement one another. A well-designed workflow does not present them as equivalent or reduce different results to a generic “verified content” badge.
The Code of Practice turns transparency into operational measures
The Code of Practice on Transparency of AI-generated Content, published in June 2026, translates the obligations into operational measures for providers and deployers. Adherence to the Code is voluntary, while the requirements under Article 50 are legally binding.
The European Commission and the AI Board have assessed the Code as an adequate tool for demonstrating compliance. That assessment does not make adherence conclusive proof of compliance: an organisation must still implement the measures that are relevant to its specific situation correctly.
For formats that can carry metadata, the technical model described in the Code combines several mechanisms. Metadata about AI generation or manipulation can be digitally signed and, where possible, linked to tamper-evident time references. Watermarking, detection tools, fingerprinting and logging can reinforce the system, particularly when content passes through transformations that remove some embedded information.
Is C2PA mandatory for complying with the AI Act?
No. The AI Act does not name C2PA as the only mandatory standard, nor does it prescribe a single implementation for every provider.
The Regulation defines the expected outcome: machine-readable marks and solutions that are detectable, interoperable, robust and reliable. The Commission’s guidelines and the Code help organisations interpret and apply these requirements, while allowing compliance through other adequate means.
C2PA is relevant because it provides an open structure for linking an asset to signed claims about its provenance. A manifest can describe origin, tools used, actions performed, ingredients and relationships with other versions. The signature and content bindings can then be used to check the declared issuer and the link to the specific content.
Using C2PA can therefore contribute to a compliant solution, but compliance depends on the entire system: format coverage, marking quality, preservation across the content supply chain, handling of exceptions, disclosures to people and the verification capabilities actually available.
Why multiple layers are needed: metadata, watermarks and detection
No technology remains equally effective at every stage. Embedded metadata may be removed by a platform, conversion or export process. An invisible watermark may survive some transformations more effectively, but its performance depends on the algorithm, the content modality and the tool used to detect it.
This is why the Code takes a layered approach. Signed metadata and watermarking can reinforce one another; fingerprinting, logging and detection tools can provide additional signals. Their results must remain distinct: finding a perceptual match is not the same as verifying the signature on a credential.
Preserving existing marks also matters. When content is edited, the new tool should avoid intentionally deleting provenance information and, where the workflow permits, add another verifiable step to the history.
The chain might look like this:
- create or capture the content;
- record information about its origin;
- sign and mark that version;
- edit it with a compatible tool;
- add a new claim about the actions performed;
- publish and verify the distributed copy.
The question is no longer only “was this content generated by AI?” but “where did this version come from, which tools changed it and which claims can we verify?”
Deepfakes: invisible metadata is not enough
For deepfakes, the information must be communicated clearly and perceptibly. Relying only on hidden metadata would require people to use a technical tool and would not fulfil the purpose of a visible disclosure.
The EU icons distinguish fully AI-generated content from content that has been partially modified. The Commission recommends accompanying the icon with a plain-language label, making it available from the first exposure and ensuring accessibility. Specific rules and exceptions remain for evidently artistic, creative, satirical and similar works.
For a platform or publisher, this means coordinating the interface with the file: the visible badge should be consistent with the technical information available, without promising more than the system can demonstrate.
A practical pipeline for businesses and platforms
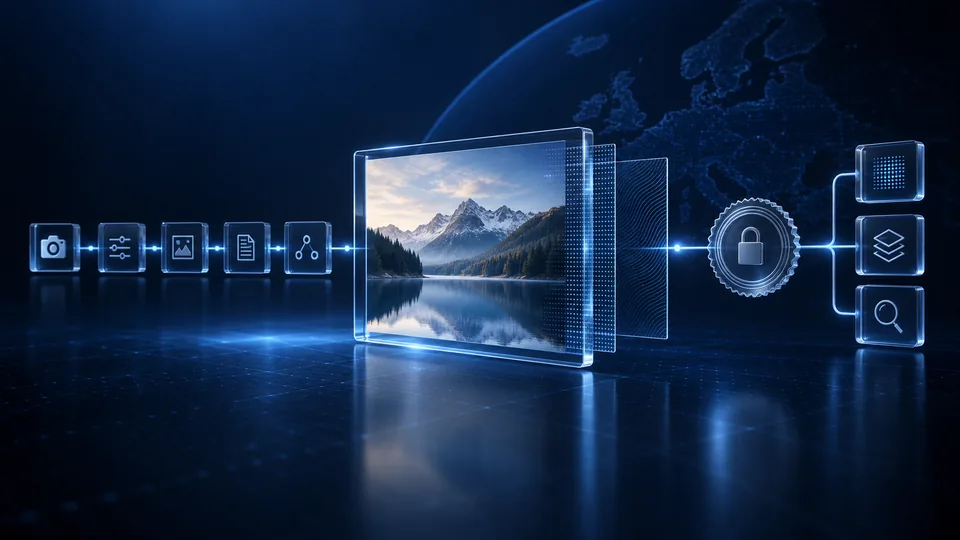
Compliance is not a matter of adding a label at the end of the process. A transparency pipeline can include:
- classifying content generated or manipulated with AI;
- distinguishing the responsibilities of providers and deployers;
- generating provenance metadata;
- adding digital signatures and time references;
- applying C2PA marking or an equivalent technology;
- using watermarking that can withstand the expected transformations;
- preserving information during editing and distribution;
- automatically checking the copy that is actually published;
- providing a visible, accessible badge or disclosure for people;
- logging results and managing versions.
Testing should cover the real distribution channels. The file stored in a DAM or CMS may differ from the version recompressed by a CDN, downloaded from a website or shared through a platform. Verification should therefore include the final distributed copy.
Frequently asked questions
Does the AI Act require every company to use C2PA?
No. The applicable obligations depend on the organisation’s role, the system and its use. C2PA is one possible technical component, not the only standard mandated by the Regulation.
Does a Content Credential prove that content is true?
No. It makes it possible to verify signed provenance claims and their link to an asset. It does not automatically prove that a scene is real, that a caption is accurate or that every edit has been documented.
Is an “AI-generated” badge sufficient?
Not for every obligation. Visible disclosure and machine-readable marking have different audiences and functions. A project may need both.
What happens if a platform removes the metadata?
The distributed copy may no longer contain the embedded credential. A layered system can use watermarks or other complementary mechanisms, but it must communicate precisely which signal was found and which verification succeeded.
Where to begin
The first step is to map the content and its technical journey: which systems generate or modify the assets, which formats they use, where the assets are signed, which transformations the CMS and CDN apply, and what information the end user sees.
Only after completing this map does it make sense to select C2PA, watermarking, detection and disclosure interfaces. The direction of the AI Act is clear: transparency must be built into the process, readable by machines and understandable to people.
This article provides a technical and editorial overview and does not constitute legal advice. Involve your legal and compliance teams when assessing the obligations and exceptions that apply to your specific circumstances.
Sources and further reading
Technical and editorial references consulted for this guide. Examples are illustrative and do not document real cases or specific integrations.
- EUR-Lex — Regulation (EU) 2024/1689, Article 50
- European Commission — Code of Practice on Transparency of AI-generated Content
- European Commission — Guidelines on the transparency obligations under Article 50
- European Commission — EU icons for labelling AI-generated content
- C2PA — Technical Specification 2.4 and guidance